Three-way reconciliation
Ledger against processor file against bank statement, daily from the first transaction, with an aged break queue and one named owner.
Core integration, payment rails, a double-entry ledger, three-way reconciliation, KYC and AML, lending and card issuing. Built for banks and licensed fintechs, against the rails and the rulebook of the market you are licensed in.
Tell us what you are building
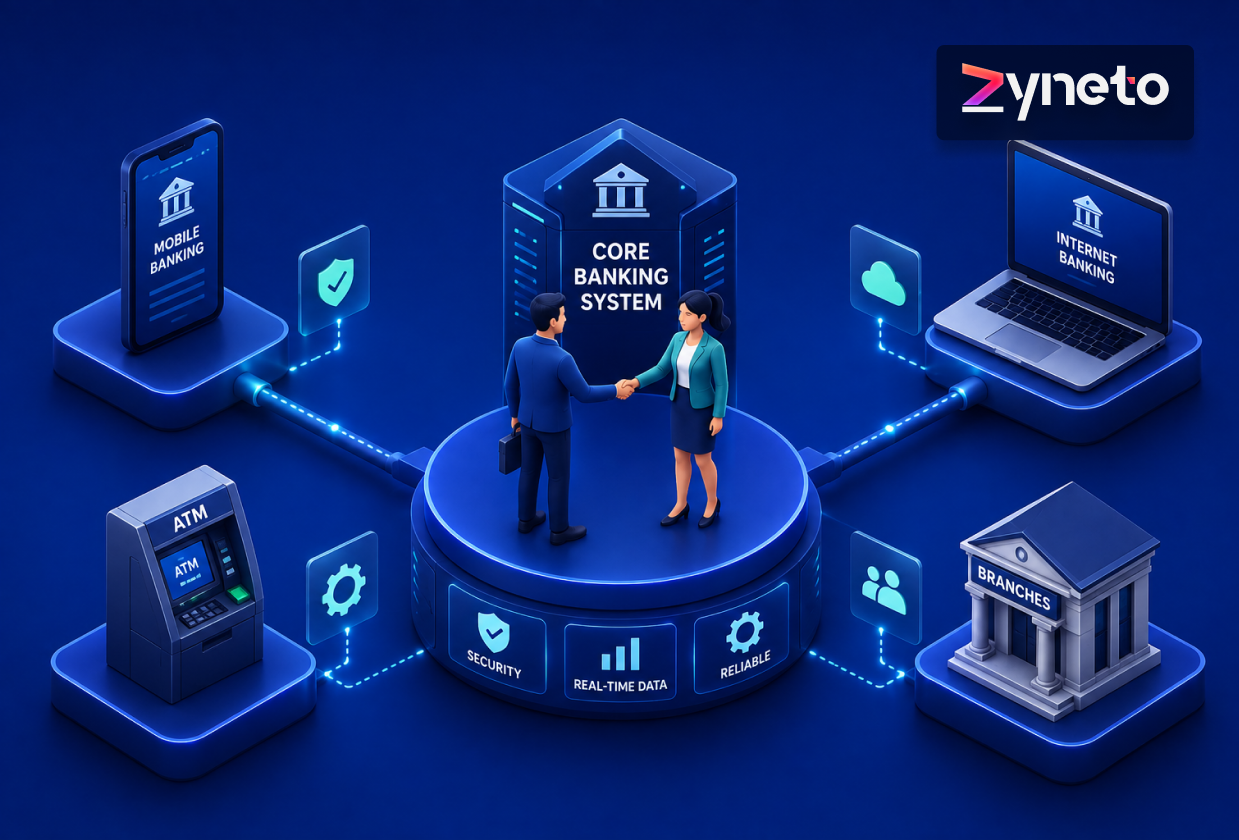
Fintech and banking software development connects a core banking system to payment rails, then proves every movement reconciles. It covers the double-entry ledger, three-way reconciliation, KYC and AML screening, card issuing and lending. The constraint is rarely the code. It is the licensing, the certification calendar and the date each rule starts to apply.
Our work
We built BankSathi, an Indian platform where users compare and apply for credit cards, savings accounts, loans, insurance and investments across several providers, with an advisor layer where users earn commission by recommending products. It runs on Next.js, Node.js and PostgreSQL, with Terraform for infrastructure and Grafana and Prometheus for metrics. What we have not done: migrated a core banking platform, or delivered a live SWIFT integration. We hold no PCI DSS attestation, no SOC 2 report and no ISO 27001 certificate. If what you need is a vendor who has already cut over a FLEXCUBE estate, that is a fair requirement and we are not it. The two builds below are the closest money-handling work we can link to.
Scope
Eight pieces of work. A rail or a core named below is one we scope and build against, not a claim of past delivery: what we have and have not delivered is in the section above.
Ledger against processor file against bank statement, daily from the first transaction, with an aged break queue and one named owner.
One rail at a time: SWIFT, Nacha ACH, FedNow, RTP, SEPA Instant, Oman RTGS, UAE Aani, Saudi sarie or India UPI. ISO 20022 for interbank messaging, ISO 8583 over a socket for cards. Each rail brings its own certification calendar.
A low-latency authorisation service with a deterministic fallback instead of a timeout, network tokens through Visa VTS or Mastercard MDES, and an issuer-processor such as Marqeta or Galileo in the path.
Profit rate, ibra' rebate and Hijri accrual are engine changes rather than configuration, and the schedule needs Sharia board sign-off.
Mechanism
Six states. Most reconciliation trouble is a team that built four and met the other two in production.
Limits, balance and sanctions screening. A decline is a terminal state with a reason code, not an empty response.
A pacs.008 out, a pacs.002 back with a status. Pending is a state, not a failure, and confusing the two duplicates sends.
A debit and a credit carrying the end-to-end transaction reference. Without it you cannot say where a payment is.
The camt.053 end-of-day statement is what you reconcile against. A camt.054 is advice, not proof of settlement.
A pacs.004 return, a partial reversal, a force post with no matching authorisation. Each is a reversing entry, never an edit.
Failure modes
Three we have hit or inherited often enough to name.
PCI DSS
The SAQ follows your integration pattern, not your volume. Ten types exist under v4.0.1, per the PCI Security Standards Council document library. These five are where a design lands.
| Your integration pattern | The form it points at | What that changes for the build |
|---|---|---|
| Full redirect to the provider's hosted page | SAQ A | No part of the payment page comes from your code. Requirements 6.4.3 and 11.6.1 left SAQ A on 31 March 2025, per the Council, but ASV scanning still applies. |
| The provider's form embedded in your page, for example in an iframe | SAQ A, plus the script eligibility criterion | The Council replaced those two requirements in SAQ A with a criterion that your site is not susceptible to script attacks, and its FAQs apply that to an embedded form, not a redirect. |
| Your own code builds, scripts or styles the payment page, or controls the redirect | SAQ A-EP | The row that surprises people. No account data reaches your servers and you are still A-EP, because you affect the integrity of the accepting page. |
| Account data reaches your servers, queue, ledger or logs | SAQ D for merchants | Every requirement is in scope and the scope map becomes the project. Tokenise at the edge so this row never applies to you. |
| You are a service provider rather than a merchant | SAQ D for Service Providers | Per the Council's FAQ it is the only SAQ open to a service provider, so a platform processing for merchants cannot validate on a short form. |
We are not a qualified security assessor and this is not an assessment: your acquirer or assessor decides the form. One caveat, stated rather than hidden. The v4.0.1 SAQ documents sit behind a click-through licence, so the lines above are paraphrased from the Council's announcements and FAQs and from the ungated v4.0 editions. Open the v4.0.1 documents before you commit a design. See also what a SOC 2 Type II involves and when to start it.
Dates
Naming an instrument is the easy part. When it starts to apply is what changes a delivery plan, so every row below carries its date, its source and the date it was last read, and the row with no date says so.
| Instrument | What it forces the software to do | Applies from, and where the date comes from |
|---|---|---|
| PCI DSS v4.0.1 and its 51 future-dated requirements | The only active version, and all 51 of the once future-dated requirements now count in an assessment. | Published 11 June 2024, requirements mandatory from 31 March 2025, v4.0 retired 31 December 2024. Per the PCI Security Standards Council, whose FAQ asks whether v4.0.1 moved that date and says it did not. Read 13 November 2026. |
| PCI DSS Requirements 6.4.3 and 11.6.1 | Inventory and justify in writing every script that loads on a payment page, and detect tampering with the page and its HTTP headers as the browser receives them, at least weekly. | Both from 31 March 2025, per the Council's guidance on the e-commerce requirements effective after that date. The SAQ A treatment is in the table above. Read 13 November 2026. |
| SWIFT CBPR+ MT and MX coexistence | Cross-border payment instructions are generated and consumed as ISO 20022 MX. Translation is contingency, not architecture. | Coexistence ended 22 November 2025, per Swift's own ISO 20022 payments guidance. Read 13 November 2026. |
| Regulation (EU) 2024/886: instant payments and verification of payee | Offer receiving, then sending, of euro instant credit transfers. Check the payee name against the account identifier after the payer enters it and before authorisation is offered, on every channel, free of charge. That changes the payment form, not the back office. | Euro area credit institutions, all passed: receiving 9 January 2025, sending and payee verification 9 October 2025. Still to come: non euro area receiving 9 January 2027 and sending with payee verification 9 July 2027, and euro area payment and e-money institutions 9 April 2027. Per the regulation. Read 17 November 2026. |
| Regulation (EU) 2022/2554 (DORA), Article 30 | As an ICT third party to an EU financial entity, one written downloadable contract naming the functions, whether a critical function may be subcontracted, the countries of processing, data return on exit, and incident assistance. | Applying since 17 January 2025, per the regulation. Read 17 November 2026. |
| PSD3 and the Payment Services Regulation, neither of them adopted | Nothing yet. Neither PSD3 nor the PSR is adopted, so there is no obligation and no date to plan against. Build to PSD2, Directive (EU) 2015/2366, which is in force. | No application date exists for PSD3 or the PSR, because neither has been adopted. Both sit at Awaiting Parliament 2nd reading on the European Parliament's legislative observatory, procedures 2023/0209(COD) and 2023/0210(COD): Council position published 5 November 2026, committee referral for second reading announced 12 November 2026. |
| India: RBI card-on-file tokenisation and payment data storage | Only the issuer and the network may store actual card data; you keep the last four digits and the issuer name. A token is unique to card, requestor and merchant together. All payment system data is stored only in India. | Tokenisation from 1 October 2022, superseding the earlier 1 January 2022 date. The storage circular is dated 6 April 2018, compliance due 15 October 2018. Per the RBI. Read 13 November 2026. |
| India: RBI E-mandate Framework, 2026 and Authentication Directions, 2025 | The issuer, not the merchant, notifies the customer at least 24 hours before each recurring debit. Those debits run without authentication up to Rs 15,000, and up to Rs 1,00,000 only for insurance premiums, mutual fund subscriptions and credit card bills. | E-mandate framework dated 21 April 2026, effective immediately, per RBI/DPSS/2026-27/396. It repeals eight earlier circulars, so a note written against the 2019, 2022 or 2023 ones is not a reliable spec. The Authentication Directions took effect on 1 April 2026 and the cross-border card-not-present validation obligation fell due on 1 October 2026. Both dates have passed. Read 13 November 2026. |
| Oman: Banking Law, CBO Decision 25/2025, IBAN and RTGS | A digital bank is defined in primary legislation, category 1 at OMR 30m and category 2 at OMR 10m paid-up capital, with different permitted activities behind each. IBAN is mandatory on international transfers, so validate it at capture. | Royal Decree 2/2025, with Decision 25/2025 effective 1 June 2025 and IBAN from 1 July 2025. Oman RTGS ISO 20022 native and 24/7 since 18 June 2023. Read 13 November 2026. |
| UAE: Open Finance Regulation | Every licensed institution and third-party provider connects through Nebras Open Finance LLC rather than bank by bank, and service-initiation rights were added. DIFC and ADGM sit outside the onshore rules. | Circular 7 of 2023, updated by Circular 3 of 2025 and in force from 10 July 2025. Read 13 November 2026. |
| Data protection across the markets on this page | Oman PDPL, with cross-border transfer controlled by MTCIT. Saudi PDPL, with SDAIA standard contractual clauses. India's DPDP Rules, CERT-In six-hour breach reporting and 180-day in-country log retention. | Oman PDPL fully enforceable from 5 February 2026. Saudi PDPL since 14 September 2023. India's DPDP Rules notified 14 November 2025. Read 13 November 2026. |
Two absences stated rather than inferred. Swift changed the SR2026 timeline on 27 August 2026 and has published no replacement date for the structured postal address mandate, so we quote none. And no PCI DSS attestation, SOC 2 report or ISO 27001 certificate carries our name. On the security work underneath, see the security checklist we hold our own backends to.
Transparency
Five drivers move the total and five modules make up the control core, in hours, so you can argue with any line. A fixed price follows discovery.
Control core
1,380 to 2,600 hours
Onboarding, ledger, one rail, reconciliation, back office
Typical timeline
14 to 22 weeks
Register to a penny test on one live rail
Delivered hours
1,587 to 3,250
After the QA and certification uplift
| Driver | Hours |
|---|---|
| Number of money railsPlus that rail's certification calendar | 180 to 350 each |
| Migration data qualityAccruals, escrow and memo codes nobody can explain | 300 to 900 |
| Core system and its integration surfaceThe protocol matters more than the vendor name | 150 to 400 |
| Conventional or Islamic product logicProfit rate and Hijri accrual are engine changes | 120 to 350 |
| Number of markets in scopeEach regulator adds reporting and residency duties | 100 to 300 each |
| Module | Hours |
|---|---|
| KYC and KYB onboarding with identity orchestrationAdd 100 or more for a review console | 250 to 450 |
| Double-entry ledger and posting engineThe highest-risk module here | 400 to 800 |
| Payment rail integration, one railEach extra rail is the same again | 180 to 350 |
| Reconciliation and break managementThree-way, daily, from day one | 250 to 450 |
| Back office console with access control and audit logMost often left out of quotes | 300 to 550 |
Delivery
Four artifacts, not four stages in a waterfall, so you can ask to see one. A migration adds a fifth: both systems in parallel, a month of history replayed, sign-off balance to the penny.
Phase 01
Every system, its protocol, its authentication, its sandbox status, its cutoff and blackout windows, its certificate expiry dates, and a minor-unit table per currency.
Phase 02
Chart of accounts, posting rules, the payment state machine with terminal states, the idempotency policy, the ISO 20022 field map and the exception catalogue, as schemas.
Phase 03
Real money on one live rail with real credentials against real cutoffs, inside the first month where the partner allows it. The evidence is the trace, the posting and the match.
Phase 04
Reconciliation runbook, break queue owners, access matrix, data flow diagrams, retention policy, log-scrub assertions in CI and disaster recovery results.
A full redirect points at SAQ A, and so does an embedded provider form, except that the Council replaced requirements 6.4.3 and 11.6.1 in SAQ A with a script-attack eligibility criterion its FAQs apply to an embedded form rather than a redirect. Once your own code builds or scripts the payment page you are in SAQ A-EP, even with no account data on your servers. Your assessor decides, and we are not one.
Build to PSD2, Directive (EU) 2015/2366, because it is the directive in force. Neither PSD3 nor the PSR has been adopted and no application date exists for either: both sit at Awaiting Parliament 2nd reading on the European Parliament's legislative observatory, procedures 2023/0209(COD) and 2023/0210(COD). Nobody can give you a PSD3 deadline today, so if a vendor quotes one, ask which published article it comes from.
PCI DSS v4.0.1 where cards are in scope, ISO 20022 and ISO 8583 for messaging, PSD2 in Europe, DORA Article 30 where we are an ICT third party to an EU financial entity, the RBI directions in India and the CBO and CBUAE rules in the Gulf. The date each applies from is in the table above, because a standard without its date is not a plan.
CBPR+ MT and MX coexistence ended on 22 November 2025, per Swift's own ISO 20022 payments guidance, so cross-border payment instructions are generated and consumed as MX. Translation belongs in your contingency plan, not your architecture. On structured postal address, Swift changed the SR2026 timeline on 27 August 2026 and has published no replacement date, so ask your service bureau rather than a vendor page.
Yes, and that is the normal case. FLEXCUBE exposes SOAP gateways over JMS and MDB plus a Java and EJB layer, Finacle uses Finacle Integrator, BaNCS is web services, and older estates use file drops over SFTP. The real constraint is the blackout window where the core rejects writes, which decides whether your integration layer holds its own state.
The control core of onboarding, ledger, one rail, reconciliation and back office is 1,380 to 2,600 hours, and 1,587 to 3,250 with the 15 to 25 percent QA and certification uplift. Fourteen to twenty two weeks as a squad. The module breakdown is above and a fixed price follows discovery.
Ask us for a PCI DSS attestation of compliance, a SOC 2 report or an ISO 27001 certificate and we have none to give you. SOC 2 is an attestation examination reported on by a CPA firm under AICPA standards, so no SOC 2 certificate exists for any firm to hold. What we hand over is what your assessor asks for: the access matrix, the data flow diagrams, the retention policy and the disaster recovery test results.
Three questions worth asking every vendor on your list, including us.
Anyone can list PCI DSS, DORA and PSD2. Ask when each started to apply, and where that date is published.
A vendor who cannot say whether their payment page is SAQ A or A-EP has not thought about your assessment.
A certification claim has a number and a scope statement behind it. We have neither, which is why this page says so.
Tell us what moves money today and where it stops reconciling, and we will say what to build and what to buy.
Real feedback from the people we've proudly partnered with.

Sales Director |Cintas
United States

Zyneto Global Technologies provided excellent project management and technical expertise throughout the engagement. The team was responsive, collaborative, and adaptive, ensuring the project met our expectations and set a strong foundation for future growth.

Founder & CEO |Moneteo

We engaged Zyneto to design and develop a custom web platform for Moneteo, aimed at improving project management, data tracking, and collaboration across internal teams and external partners. Their work included full-stack web development, custom modules for workflow automation, API integration, and comprehensive testing.

CEO |E-Commerce Platform

Overall, their responsiveness and timely deliveries contributed positively to the project's success. The client achieved better data management and quality. The service provider delivered the project on time and ensured prompt responsiveness throughout the engagement. Their innovative approach was outstanding.
Explore further
The BankSathi stack
Customer and agent apps
The backend
The other regulated product
Client money
Including the BankSathi build
Module by module
Failure modes to survive
Rule versus model
The report partners ask for
Engineering notes on payments, cores and the back office work behind a regulated build.