Dating App Trust and Safety: AI Moderation, Risk Scoring and Human Review


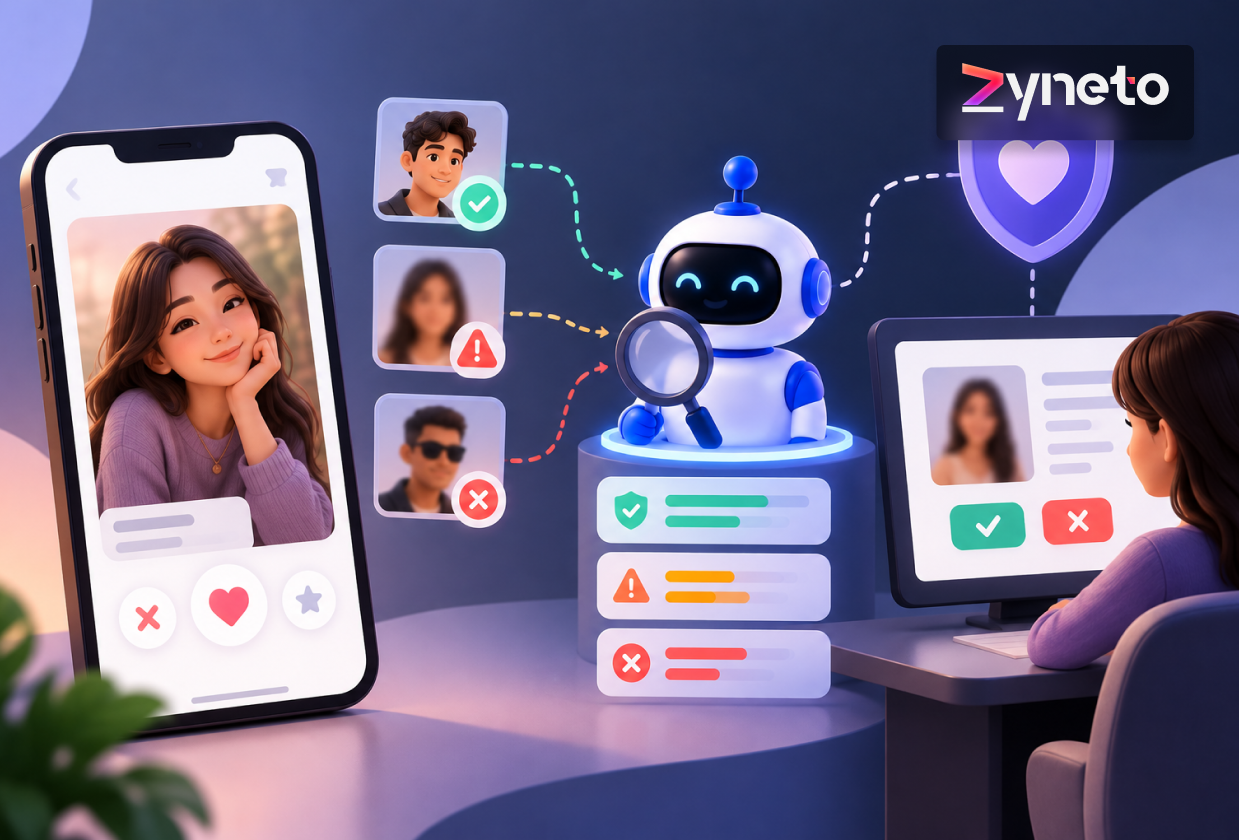
Your matching algorithm can be excellent and your app can still fail.
People rarely quit a dating app because the recommendations were poor. They quit after one bad experience nobody handled. A profile that turned out to be fake. A message that crossed a line. A report that went nowhere.
That is a trust and safety problem rather than a matching problem, and it usually decides whether an app survives its first year of real traffic.
Most teams know they need moderation. Far fewer know what to automate, what to escalate, and how to enforce rules without punishing innocent users. Those decisions shape your cost base, your legal exposure and your retention curve.
This guide covers the operating model behind dating app trust and safety. You will see which threats are worth detecting, how raw signals become risk scores, where human judgment belongs, and the order to build it in.
A dating app trust and safety system is the combined set of detection, decision and enforcement processes that decide who gets to use your platform and what they are allowed to do on it.
It is not a single feature. It is a pipeline.
Signals come in from profiles, photos, messages, payments and user reports. Models and rules score those signals. The score triggers an action. Humans review the hard cases. Every decision feeds back into the system as training data.
Three things separate a real dating app moderation system from a reporting form bolted onto an admin panel:
That last point matters more than teams expect. Regulators increasingly ask for it. So do your users, loudly, the first time you get a decision wrong.
Start by naming what you are defending against. A vague goal like “stop bad actors” produces vague systems.
UK regulator Ofcom describes the risks on dating and social discovery services under the Online Safety Act as romance fraud, intimate image abuse, sextortion, harassment, stalking and grooming. That list is a useful starting point. It reflects what actually happens at scale.
In practice the threats fall into four groups.
Fake profiles, stolen photos, catfishing and bot accounts. These are the entry point for most downstream harm, which is why fake profile detection earns its budget early.
Romance scam prevention sits here. Investment pitches, crypto pressure, emergency money requests and the slow trust-building that precedes them. Scammers are patient and they are usually working several targets at once.
Harassment, unsolicited explicit images, threats and stalking. Much of this happens in chat, after matching, where a profile-level check will never see it.
Underage accounts, grooming and child sexual abuse material. This category is different from the others. It is not a policy question but a legal one, and it needs its own escalation path.
These sit alongside the usual dating app development challenges of matching, retention and scale. Safety differs in one way though. Everything else stays where you put it. An adversary adapts to whatever you build.
A working dating app safety architecture moves through five stages, each feeding the next. Signals in, classification, scoring, enforcement, review.
You cannot score what you do not capture. The useful signals sit in four places.
Capture these from day one even if you score none of them yet. Retrofitting event logging after an incident is painful and you lose the historical baseline that makes anomaly detection work.
Classifiers label content and behaviour. A photo model flags nudity or a stock image. A text model flags sexual harassment or a money request. A behaviour model flags a pattern that looks automated.
Each classifier returns a confidence value. Nothing is a yes or no at this stage.
Individual flags are weak. Combined flags are strong.
A new account is not suspicious. A new account on a recycled device that messages forty people in ten minutes with near-identical text is a different matter. The score, not the single flag, drives the decision.
The score maps to an action, from a quiet nudge through to a permanent ban. The next section covers that ladder.
Humans handle ambiguity, appeals and anything severe. Their decisions become labelled data. That loop is what stops your models decaying as tactics change.
Build the loop early even when your volumes are small. A system without feedback gets worse every month while appearing to work.
AI dating app moderation works best when you treat it as four separate problems rather than one.
Check photos against reverse-image sources to catch stolen pictures. Run liveness and face matching for verified badges. Tinder’s Photo Verification asks users for a short video selfie and compares it to their profile photos, then lets verified users restrict incoming messages to other verified accounts through Photo Verified Chat. That second part is the clever bit. Verification becomes a benefit rather than a chore.
This is where most harm actually lands. Run classifiers on message content for harassment, explicit material and financial pressure. Watch conversation shape too. Scammers push to move off-platform fast, so sudden contact-detail sharing is a meaningful signal on its own.
Scan media in both directions. Unsolicited explicit images need blurring or blocking before delivery, not after a complaint. Hash-matching against known illegal material should run on every upload with no exceptions.
The strongest signals are rarely in the content. Look at swipe velocity, message templating across conversations, login geography that jumps continents and accounts that go quiet then wake up in a burst.
One practical warning. Models trained on general social content underperform on dating language. Flirtation reads as harassment. Slang reads as spam. Expect to fine-tune on your own labelled data. Your first six months of labels will be the most valuable asset you build.
Intervention design matters as much as detection. Tinder’s “Are You Sure?” prompt warns a sender before a likely offensive message goes out, and “Does This Bother You?” asks the recipient whether to report it. A nudge that prevents a message costs nothing and avoids a report entirely. This kind of friction-by-design now sits near the top of current dating app development trends.
Risk scoring in dating apps follows the same logic as credit risk. Weight the signals, sum them, set thresholds, then review where the thresholds land.
The common mistake is a single ban threshold. One line between fine and banned gives you two bad outcomes at once. You over-punish borderline users and under-punish sophisticated ones who stay just below it.
Use a graded ladder instead.
|
Signal strength |
Typical action |
Decided by |
Tell the user? |
Appealable |
|
Single weak signal |
In-product nudge or friction |
Automated |
In the moment |
Not applicable |
|
Moderate, no harm yet |
Rate limit, reduced reach, prompt to verify |
Automated, sampled by humans |
Yes, with a reason |
Yes |
|
Strong, recoverable |
Feature suspension pending review |
Automated, human confirms |
Yes, with a reason |
Yes |
|
Strong, serious harm |
Content removal and account ban |
Human decision |
Yes, with a reason |
Yes, fast-tracked |
|
Suspected illegal content |
Removal, evidence preservation, report to authorities |
Human plus legal counsel |
Follow legal advice |
Separate process |
Two rules make this ladder work.
Automate downward actions freely and upward actions carefully. Rate limiting a suspicious account automatically is sensible. Permanently banning one automatically is not, unless the evidence is overwhelming.
Avoid silent enforcement wherever you can. Shadow-banning is tempting because it stops complaints. It also stops feedback, hides your error rate and infuriates users who eventually work it out. Reserve it for confirmed bot networks.
Scoring also interacts with distribution. A throttled account should surface less often in recommendations, so your safety layer and your dating app algorithms need to share state rather than run independently.
Automation handles volume. Humans handle meaning.
A content moderation workflow needs three human-facing paths, and they are not the same thing.
Flagged items routed to reviewers by severity rather than arrival order. A sextortion report and a blurry photo complaint should never sit in the same line. Set separate response targets for each queue and measure against them.
Make reporting easy to find, quick to submit and specific. Vague categories produce vague data. Always confirm back to the reporter that something happened, even when you cannot share the outcome.
Every enforcement action above a nudge needs a route back. A different reviewer should handle the appeal, never the one who made the original call.
Human-in-the-loop moderation only works if reviewers have what they need. Give them the context behind a flag: which signals fired, the conversation history, the account’s prior actions. A reviewer judging a single screenshot will be wrong often.
Two things teams routinely underestimate.
False positives are expensive. A wrongly banned paying user rarely comes back and often posts about it. Track your reversal rate on appeal as closely as you track detection. A reversal rate above roughly one in ten suggests your thresholds are too aggressive.
Moderator wellbeing is an operational requirement. People reviewing abuse material need rotation, limits on exposure, blurring by default and real access to support. High turnover in a review team degrades decision quality quickly, and it shows up in your error rate before anywhere else.
Safety systems need data. Privacy law limits how you handle it. The resolution is proportionality rather than avoidance.
Scan what you must, keep what you need, delete the rest on a schedule you can defend.
Dating app identity verification carries the same tension. Document checks and face matching produce biometric data, which is a special category under GDPR and several US state laws. Verify first, then keep the verdict rather than the image wherever your provider allows it.
Be precise about what applies to you. These duties are often described more broadly than they are written.
Dating services with UK users are in scope as user-to-user services, which brings four core obligations:
The separate requirement for highly effective age assurance attaches to services that allow pornographic content, not to dating apps as a category. Where it does apply, Ofcom lists these methods as capable of meeting the standard:
Two things explicitly fail that test. Self-declared age, and any payment method that does not require the user to be eighteen.
Even where the strict duty does not apply, a tick-box age gate is weak protection. Treat strong age assurance as a product decision rather than a compliance minimum.
Legal advice here is not optional, and it is not the same as engineering advice. Get both.
You cannot build everything at launch. You can build in an order that does not need unpicking later. The sequencing is not unique to dating either, and most of what applies when you create a mobile app of any kind still holds here.
Event logging on every meaningful action. Report and block flows. A basic admin console. Hash-matching for illegal imagery. Written community guidelines you can actually enforce.
This is the floor. It belongs in the first build alongside the matching and messaging work that goes into how to create a dating app.
Add off-the-shelf classifiers for text and images. Introduce optional photo verification. Build the review queue properly with severity routing. Start labelling every human decision from this point on.
Move to risk scoring that combines signals rather than acting on each one alone. Fine-tune models on your own labelled data. Add the enforcement ladder and the appeals path.
This is also where most teams bring in a specialist mobile app development company, because the safety layer now touches ranking, payments and infrastructure at the same time.
Network-level detection for coordinated scam rings. Regional policy variation. Proactive outreach to users who look like targets rather than threats.
On budget, treat trust and safety as a permanent operating line rather than a project. Moderation cost scales with users, not features, and it rarely falls. Build it into your dating app development cost model early, because it changes your unit economics and your pricing.
Track outcomes, not activity. The number of accounts banned tells you almost nothing on its own.
That last metric is the one most teams miss. It links safety directly to retention, which is usually how you justify the budget internally.
Most teams arrive at this point the same way. The matching works, the app has users, and moderation is still a spreadsheet plus a shared inbox nobody has time to clear.
The hard part is rarely the model. It is the plumbing around it. Detection pipelines, review tooling, an enforcement ladder wired into ranking and payments, and a feedback loop that keeps the whole thing from decaying.
That engineering is what a dating app development company like Zyneto is set up to handle, including the AI components where a model genuinely beats a rule. We will also say so when a simple rule is the better answer.
If you are weighing what to build first, a scoping call is usually enough to map the sequence.
Trust and safety is an operating system rather than a feature list. Decide which harms matter most on your platform, capture the signals that reveal them, grade your responses instead of reaching for bans, and keep humans on the decisions that need judgment.
Start with logging, reporting and clear rules. Everything else builds on that foundation, and nothing works well without it.
The connected set of detection, scoring, enforcement and review processes that decide who can use a platform and what they can do there. It joins classifiers, human reviewers and an appeals route into one pipeline rather than a single feature.
It catches many, especially bulk and automated accounts, using image origin checks, text patterns and behavioural signals. Accuracy drops against patient scammers using original photos. Combining weak signals into one score beats any single detector.
Anything severe, ambiguous or legally sensitive. That covers suspected minors, grooming, sextortion, credible threats and every appeal. Permanent bans should carry human confirmation unless the evidence is overwhelming.
Grade your enforcement instead of using one ban threshold. Require human confirmation on severe actions and give reviewers full context behind each flag. Then watch the appeal reversal rate. A high rate means your thresholds are too tight.
Violation prevalence, time to action by severity tier, the share of enforcement that is proactive rather than report-driven, appeal reversal rate, repeat victimisation and whether users who report go on to churn.
Sudhanshi has several years of experience in digital marketing and now works on growth at Zyneto. Her work covers SEO, content strategy, organic lead generation, social media and paid campaigns across Google, LinkedIn, Instagram and Facebook. She has run B2B technology and SaaS campaigns for international audiences, helping brands get found in search and stay found, and works day to day in Google Analytics, Search Console, Ahrefs, SEMrush, Screaming Frog and Canva. She follows AI driven marketing, changing search behaviour, content automation and social growth closely, and turns audience and search data into plans a team can actually run. She writes about SEO, content strategy and the tactics that still earn traffic as search keeps shifting.
Share your details and we will talk soon.
Be the first to access expert strategies, actionable tips, and the trends actually shaping the digital world. No fluff - just practical insights delivered straight to your inbox.
Dive into our blog and stay ahead of the curve with expert perspectives, future-ready trends, and tech tips written for decision-makers and doers alike.